HTTP Basic Auth. [LetsDefend Challenge]
Investigating a pcap file for a potential attack.
The pcap file ‘webserver.em0.pcap’ was opened in Wireshark. The ‘http’ filter was used to filter through the logs for all http packets. There were a total of 5 HTTP GET requests (Figure 2).
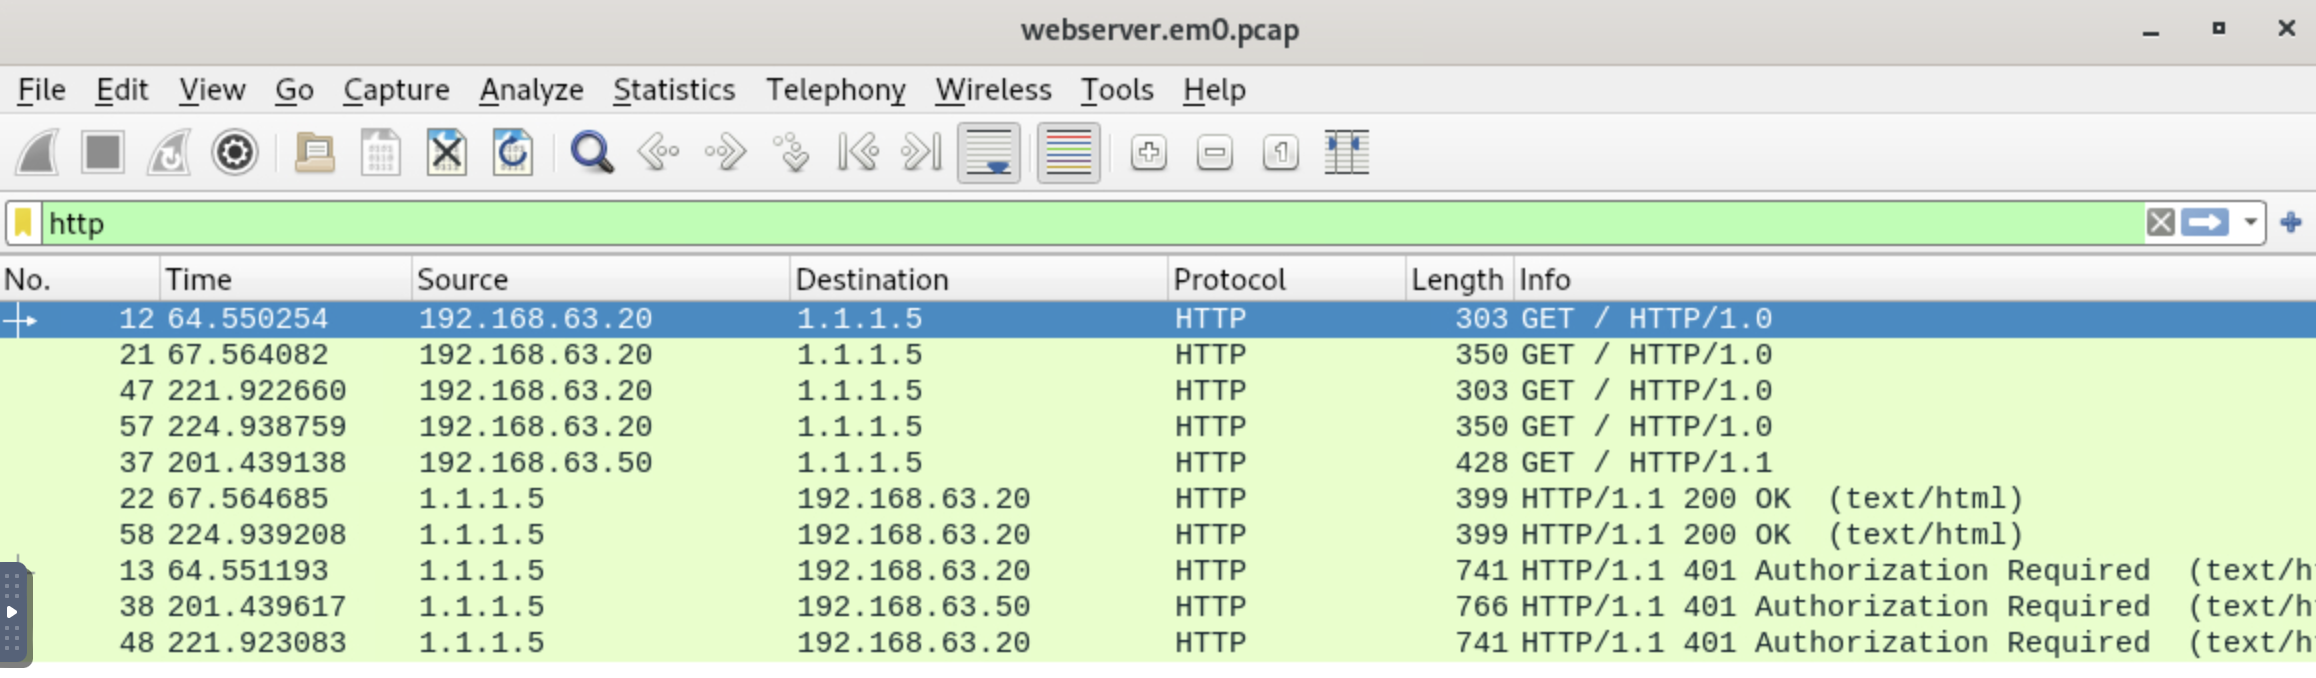 Figure 2 Filtered ‘http’ results from the pcap file
The User-agent string was Lynx/2.8.7rel.1 libwww-FM/2.14 SSL-MM/1.4.1 OpenSSL/0.9.8n. The version of OpenSSL running is OpenSSL/0.9.8n. The name and version of the server it was sent from is Apache/2.2.15. The server operating system is FreeBSD (Figure 3).
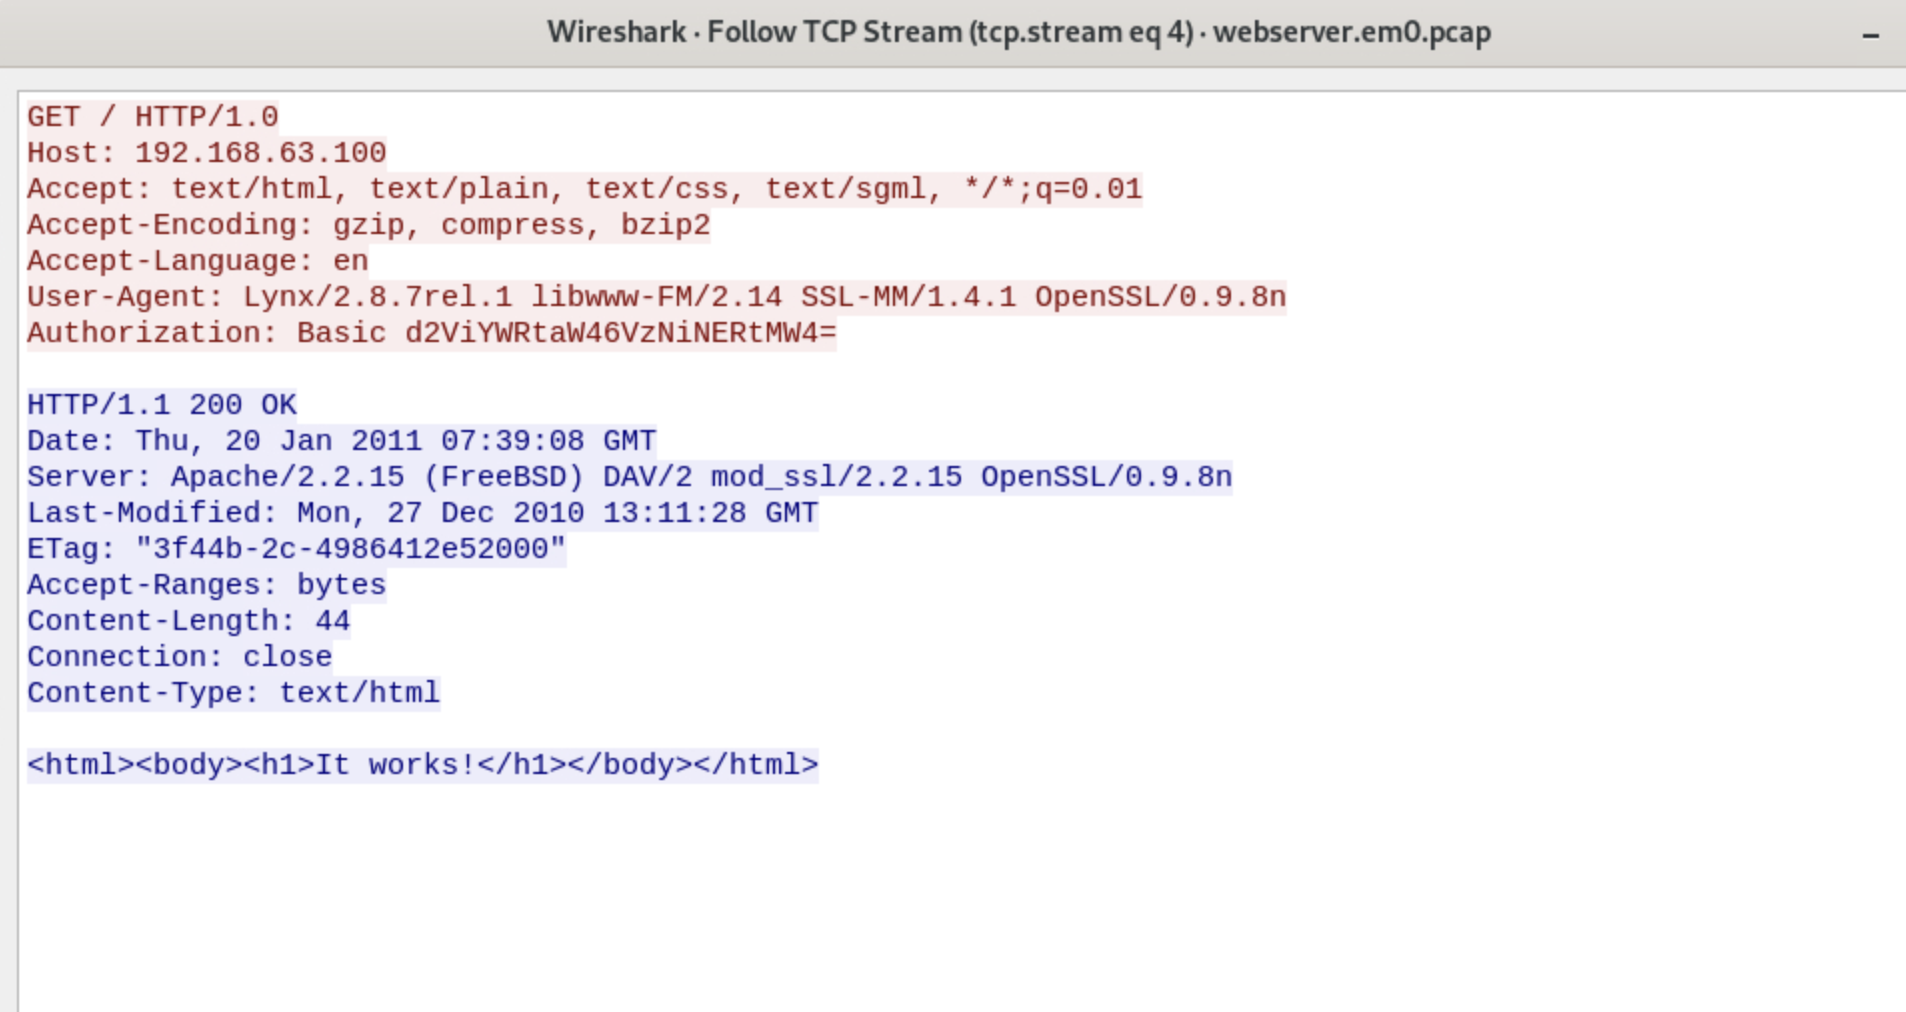 Figure 3 TCP stream of packet with response code 200
By following the TCP stream of a packet with the response code 200 (Figure 3), I was able to determine the username and password used for user authenticaiton. The string ‘d2ViYWRtaW46VzNiNERtMw4=’ was decoded from Base64, providing the username and password (Figure 4).
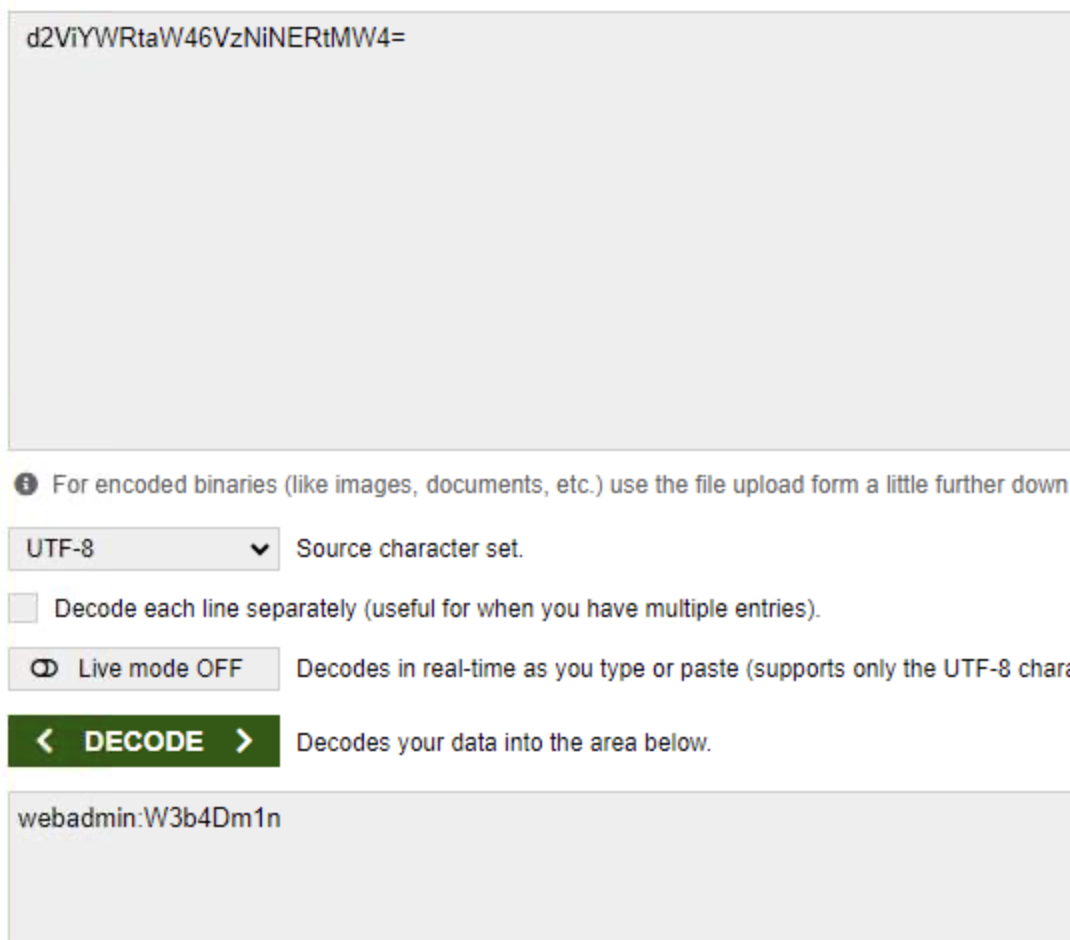 Figure 4 Decoded user authentication username and password