SOC138 EventID:77 - Detected Suspicious Xls File
Analysis of suspicious file
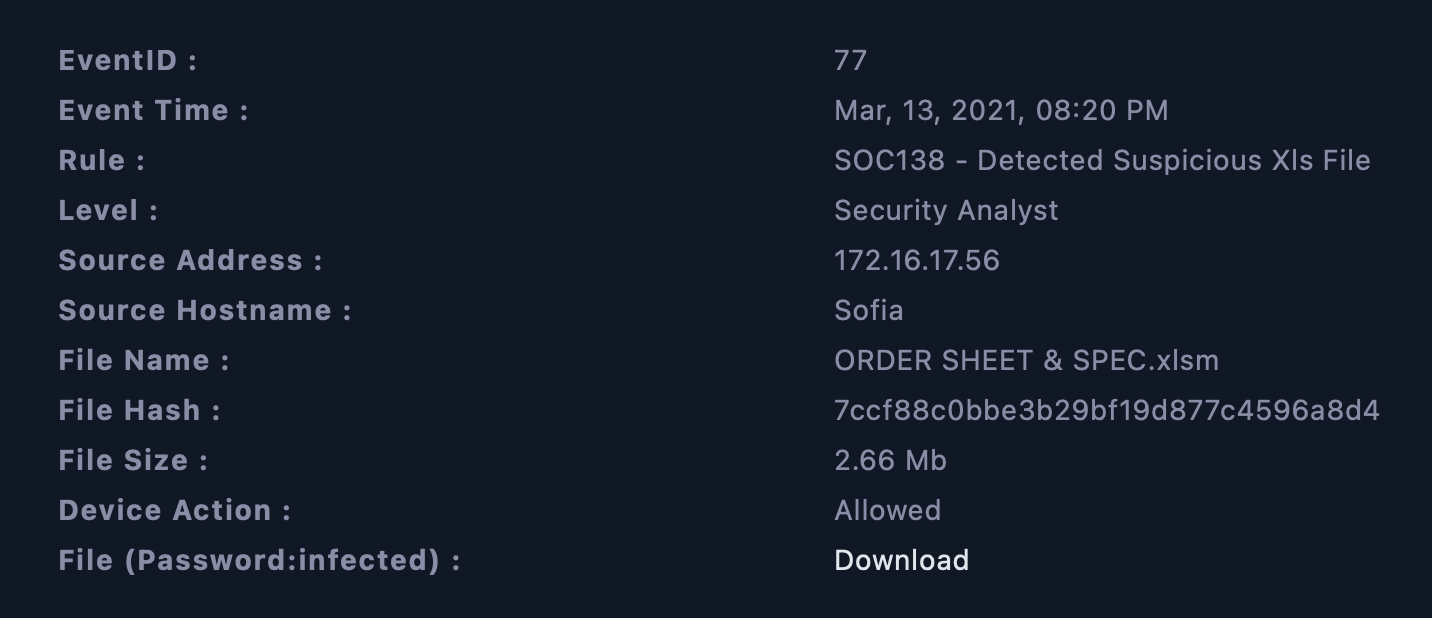 Figure 1 Screenshot of the alert
A medium alert was received March 13, 2021 at 08:20 PM. The sender’s address was 172.16.17.56. The alert contained an attachment ‘ORDER SHEET & SPEC.xlsm’, which is a downloadable file. I filtered through the logs using the source address and discovered two firewall logs related to the source address (Figure 2).
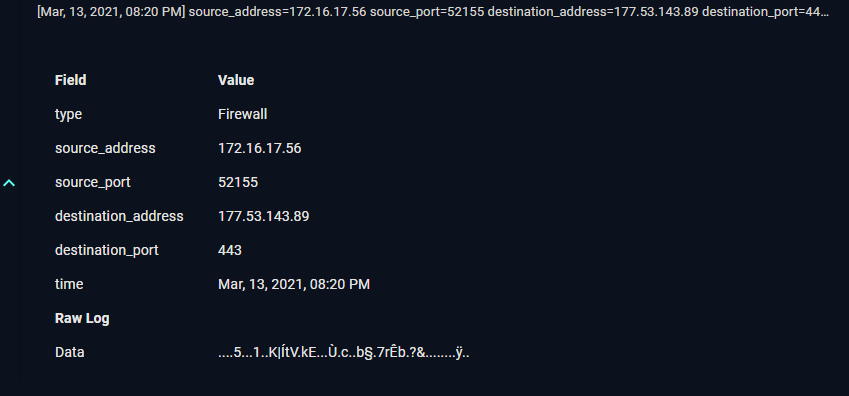 Figure 2 Screenshot of 1 or 2 Firewall logs
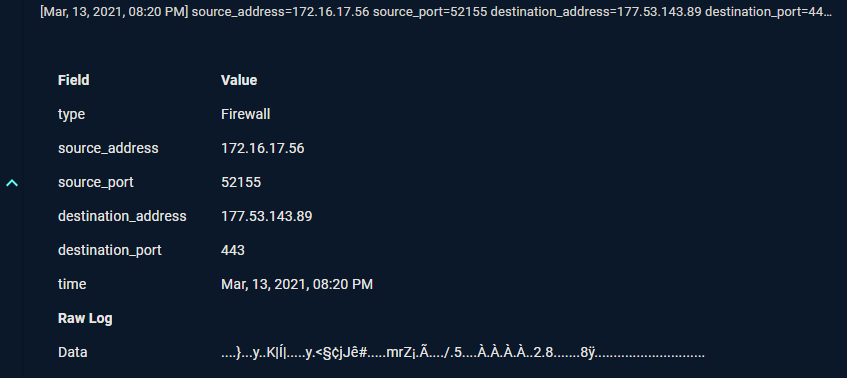 Figure 3 Screenshot of 2 of 2 Firewall logs
The destination address was analyzed in Cisco Talos Intelligence search and it was found to be based in Brazil. The destination address’s reputation is neutral (Figure 4).
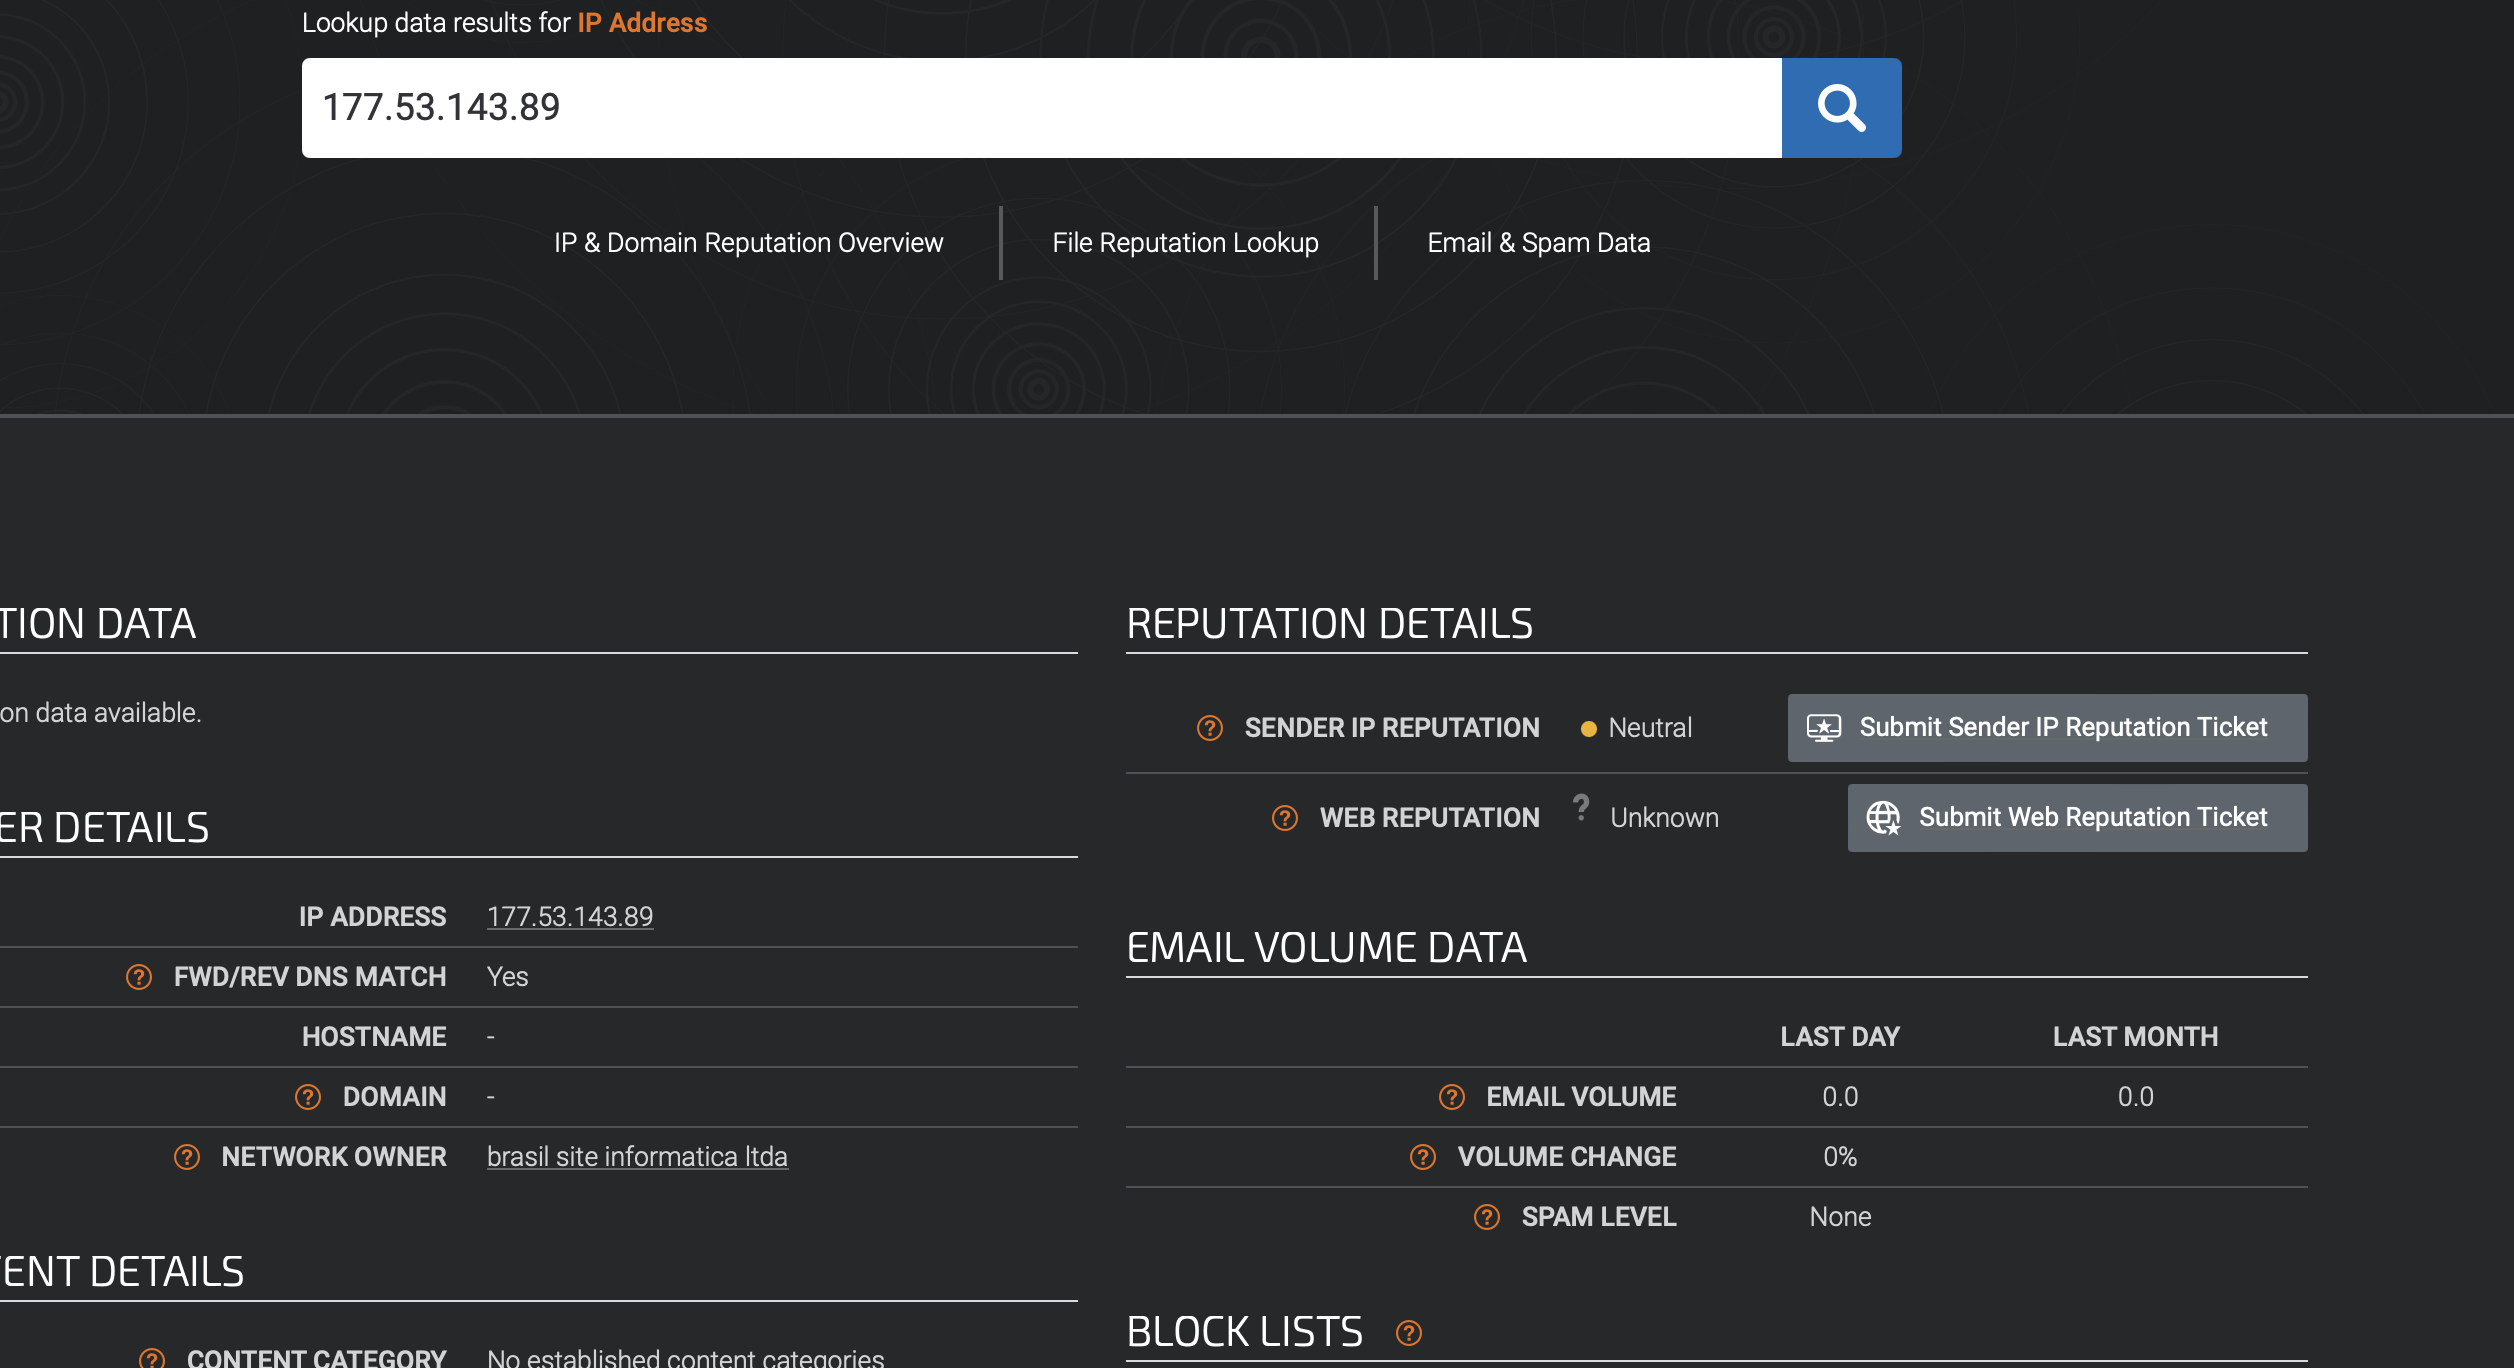 Figure 4 Screenshot of Cisco Talos Intelligence search on the Source IP
The source address was analyzed in LetsDefend’s EDR and it was discovered it belonged to primary user Sofia2020. The user’s last login was October 25, 2020 at 11:44 PM. Considering this, the user’s IP address may have been spoofed (Figure 5).
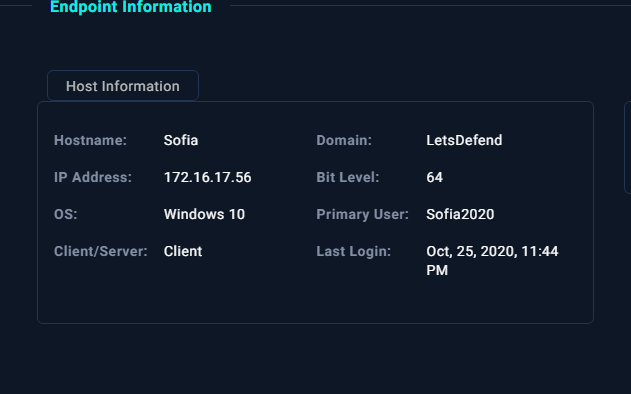 Figure 5 Endpoint information associated with the source IP
To determine if the file is malicious, I analyzed it’s file hash in VirusTotal (Figure 6) and HybridAnalysis (Figure 7). Virus Total and HybridAnalysis determined the file was malicious.
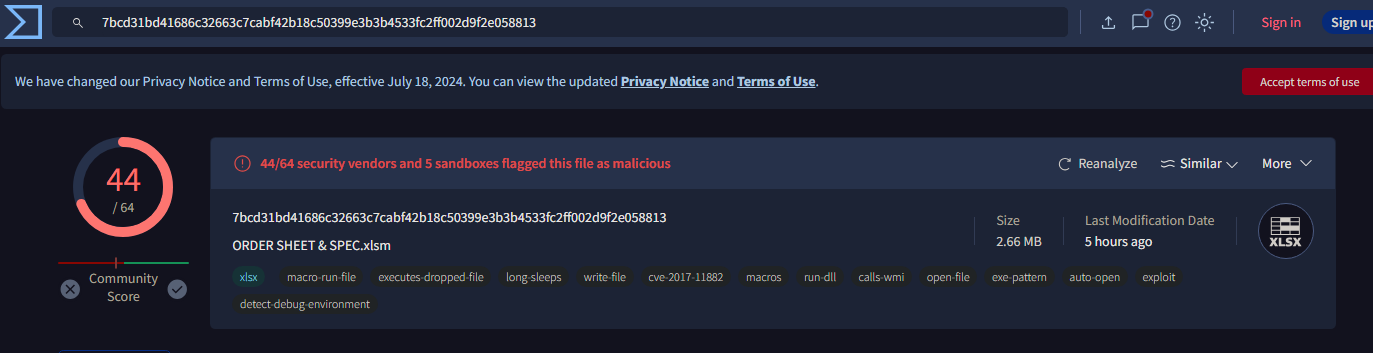 Figure 6 Analysis of file hash via Virus Total
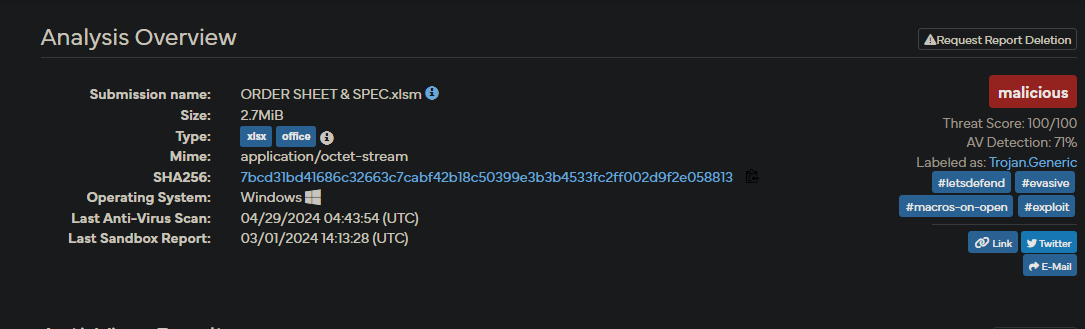 Figure 7 Analysis of file hash via HybridAnalysis
The zipped file was uploaded to AnyRun and was determined to be malicious (Figure 8). The summary indicator of compromise provided by AnyRun list multiwaretechnolgia.br as a malicious domain (Figure 9). The domain was checked in Cisco Talos (Figure 10) and it’s reputation is untrusted. The domain is based in Brazil (Figure 11).
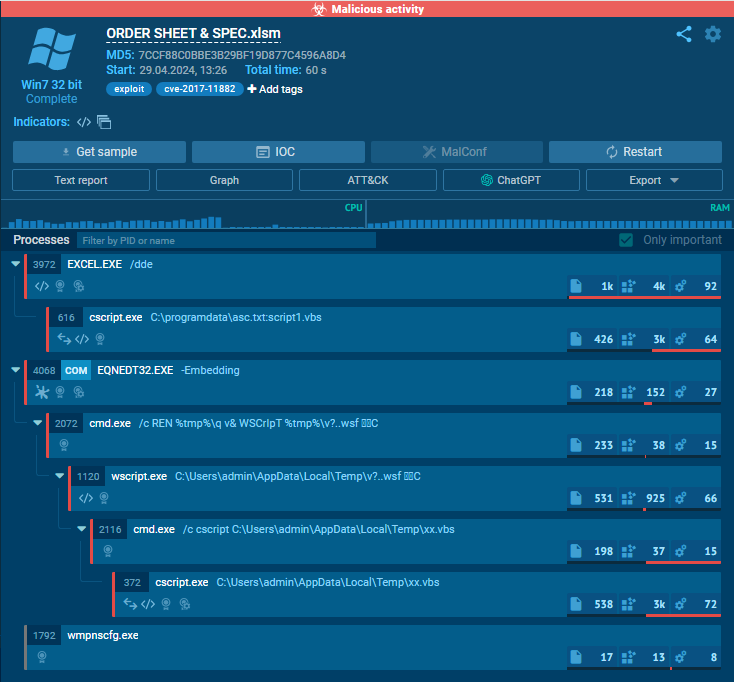 Figure 8 Analysis of file in AnyRun
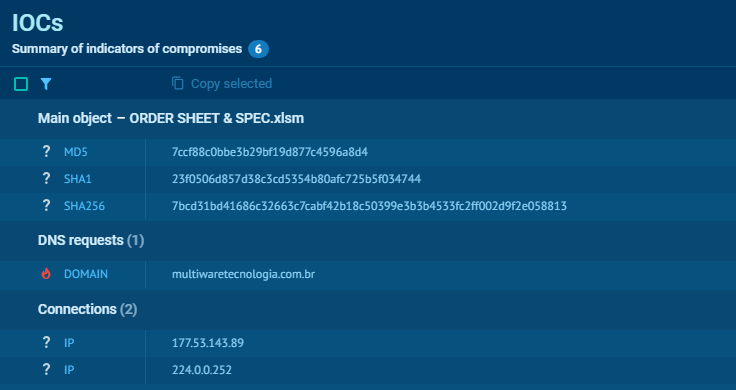 Figure 9 Summary of Inidcators of Compromise —
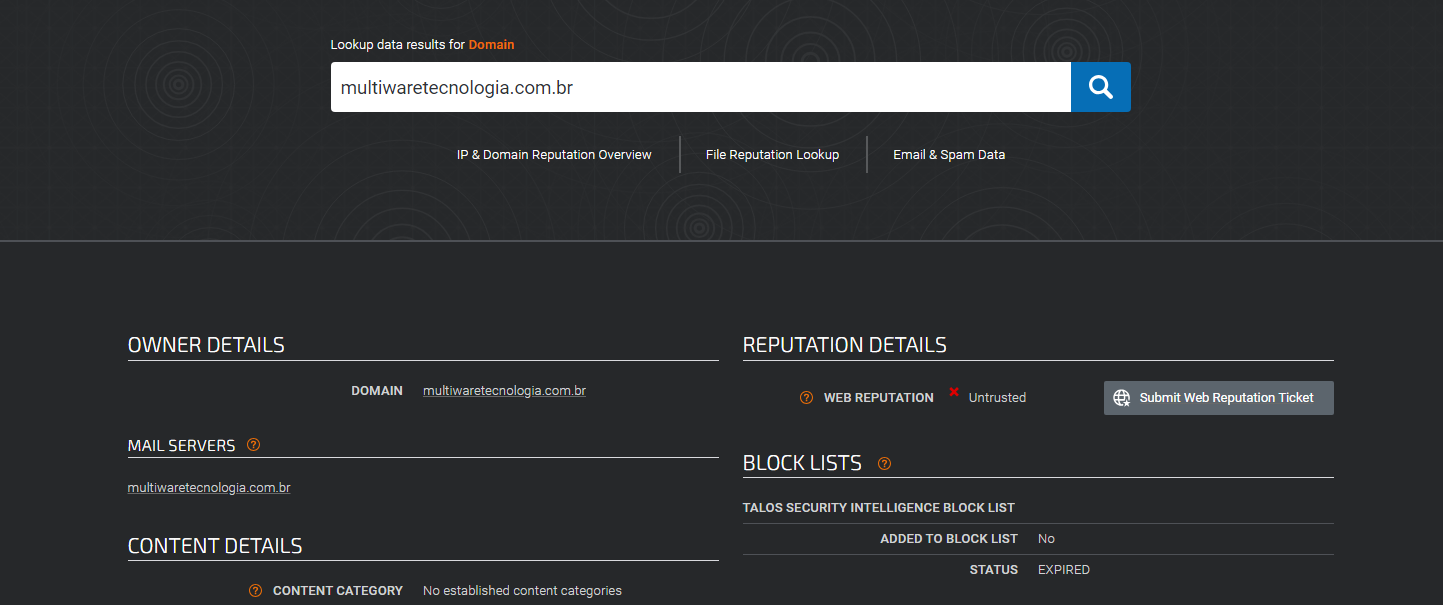 Figure 10 Domain analysis via Cisco Talos Intelligence search
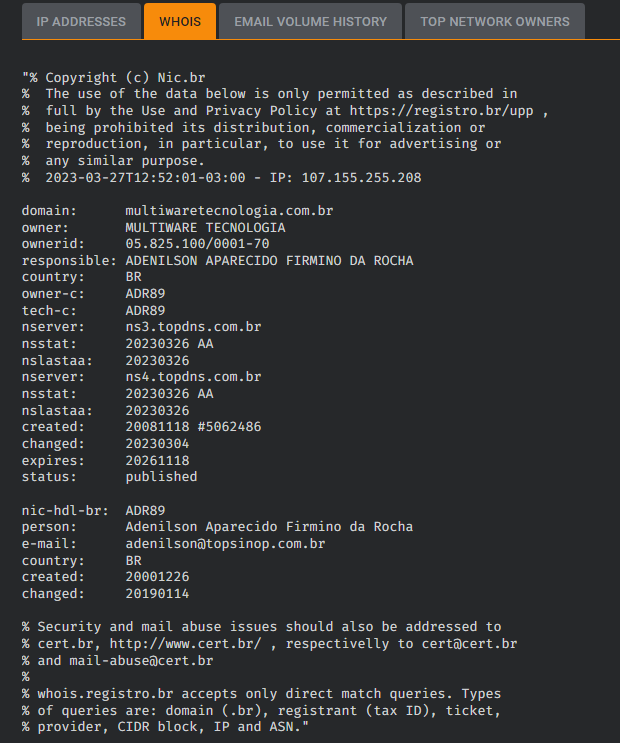 Figure 11 WHOIS analysis on the malicious Domain via Cisco Talos Intelligence
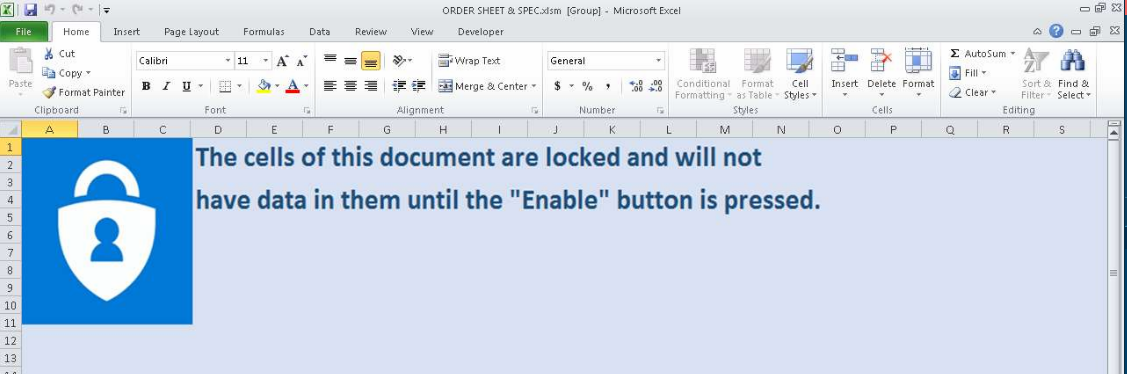 Figure 12 A screenshot from AnyRun of the opened ORDER SHEET & Spec.xlsm.
Conclusion
A medium alert was received on March 20, 2021 due to a suspicious excel file. Analysis of the source address showed the host came from within LetsDefend from user Sofia2020. The user had not accessed the computer since October 25, 2020. Therefore, the IP address was spoofed. The file’s hash was uploaded to VirusTotal and Hybrid Analysis, and was determined to be malicious. The zipped file was then uploaded into AnyRun, and also determined to be malicious. The summary of the indicators of compromise displayed a malicious domain. The domain was searched in Cisco Talos Intelligence, and found to be located in Brazil. The domain’s reputation was untrusted. Considering this, host Sofia’s computer was contained. To prevent a reoccurrence of this event, two-factor authentication should be implemented or a network firewall should be utilized. If the orginal intended user is no longer accessing the computer then the login and access should be disabled.