SOC140 EventID:82 - Phishing Mail Detected - Suspicious Task Scheduler
Analysis of phishing mail.
Severity Level: Medium
On March 21, 2021 at 12:26 PM, phishing mail was detected. It originated from source address: aaronluo@cmail.carletion.ca and it’s SMTP address is 189.162.189.159. The email’s destination address is mark@letsdefend.io. The email subject stated COVID19 Vaccine.
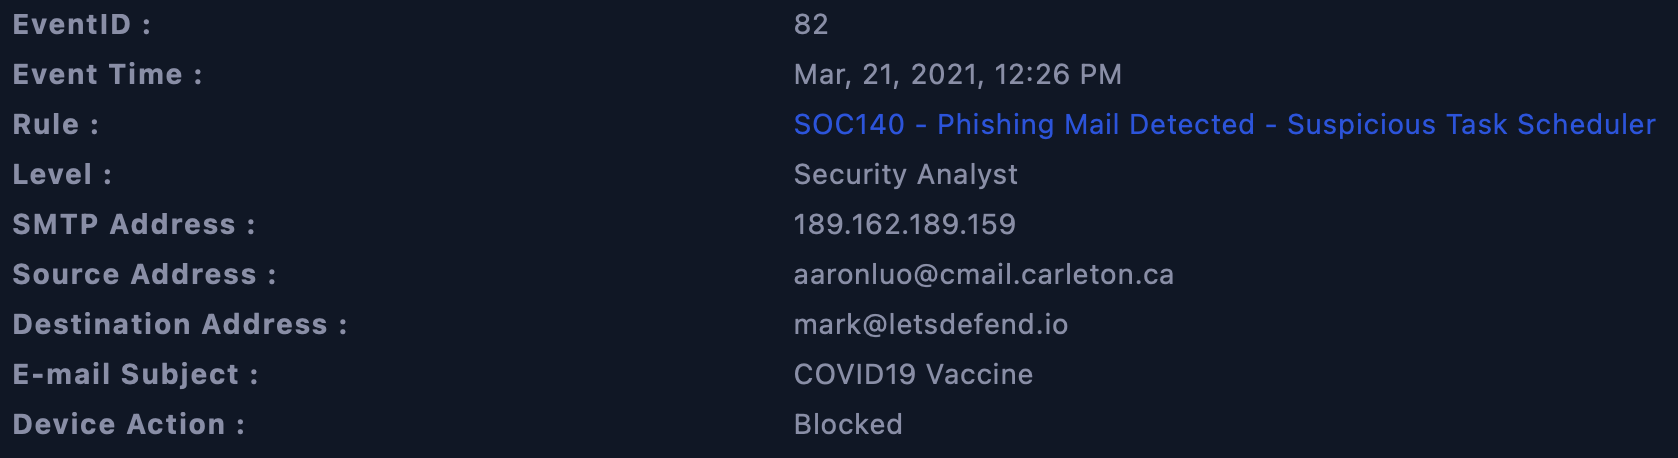 Figure 1 Screenshot of the alert
—
Further analysis of the SMTP address resulted in the discovery of the destination address 172.16.20.3.
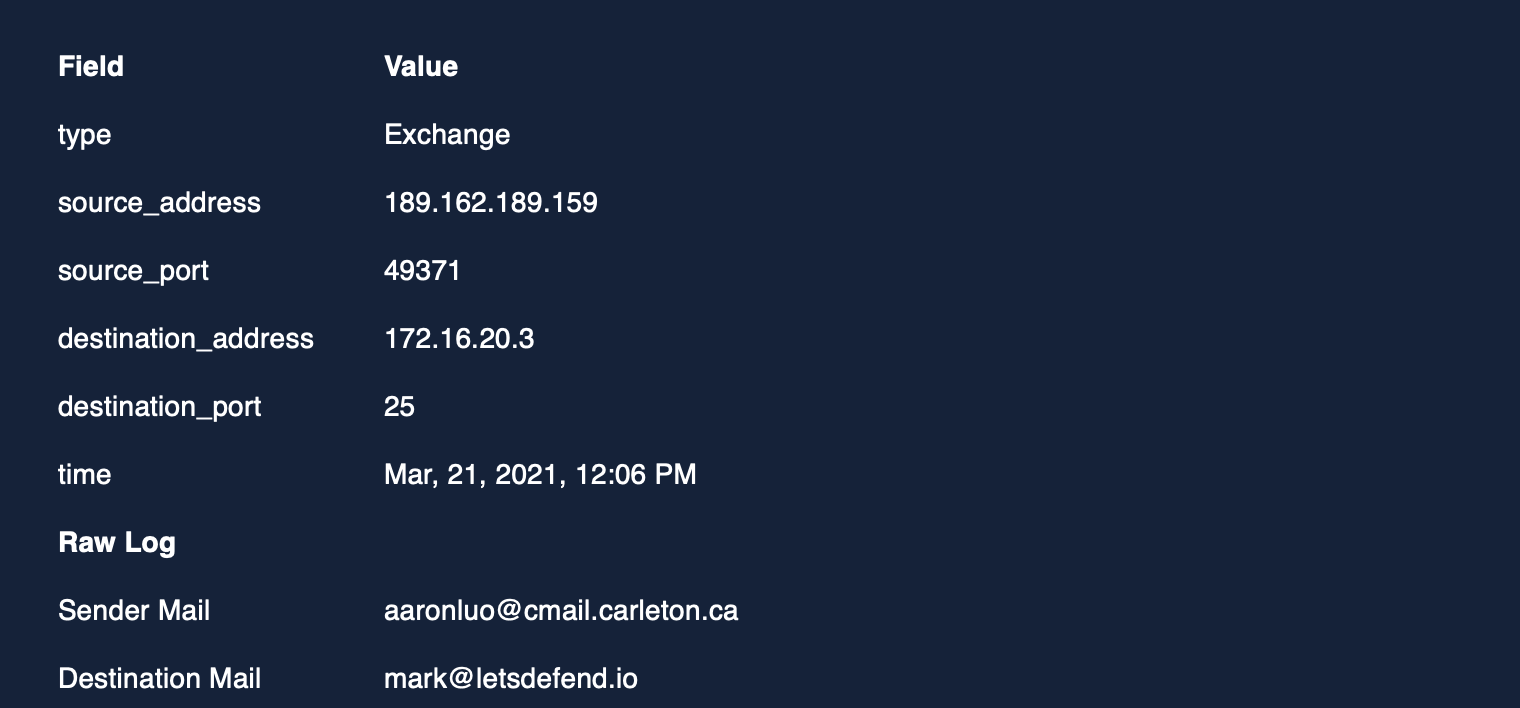 Figure 2 Screenshot of event details via the Log management dashboard
Inputting the destination address into LetsDefend’s EDR displays the host information. —
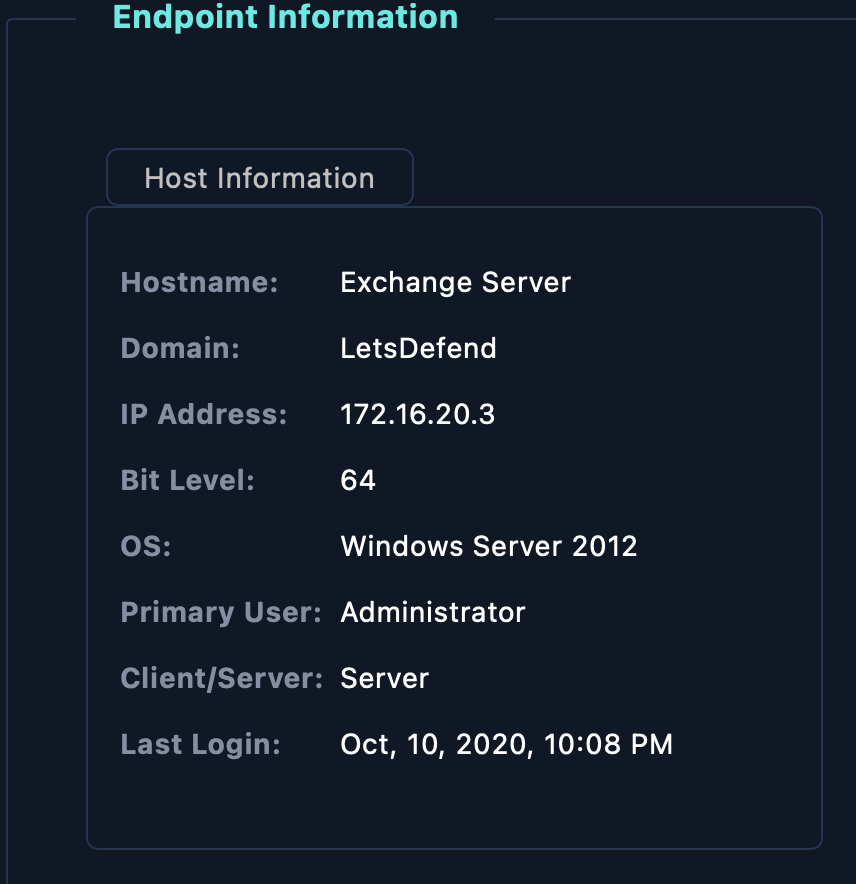 Figure 3 Screenshot of LetsDefend’s EDR
The email contained an attachment with a file hash and a password: infected. The MD5 hash is 72c812cf21909a48eb9cceb9e04b865d.
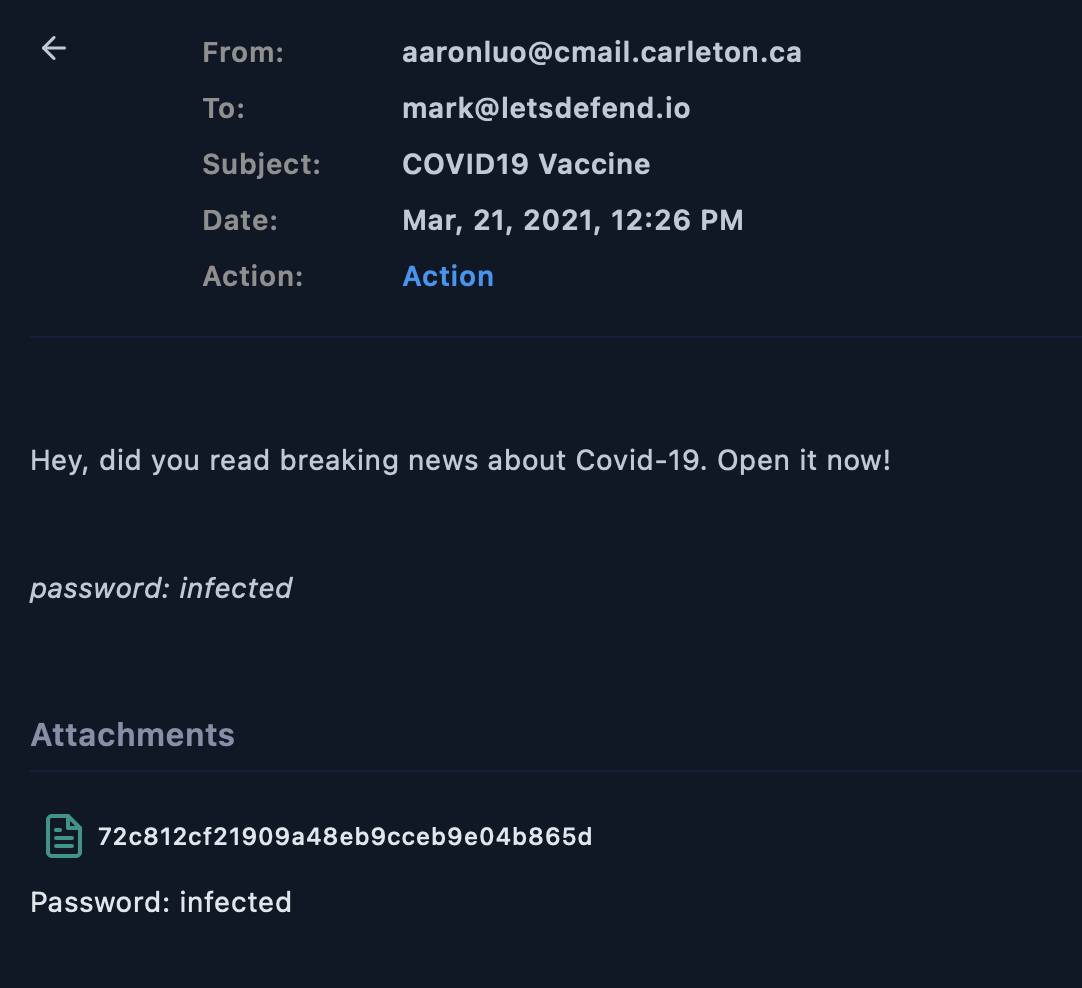 Figure 4 The suspicious email containing a file hash
The sender’s email address domain name was searched in Cisco Talos and returned the domain name belongs to an educational institution.
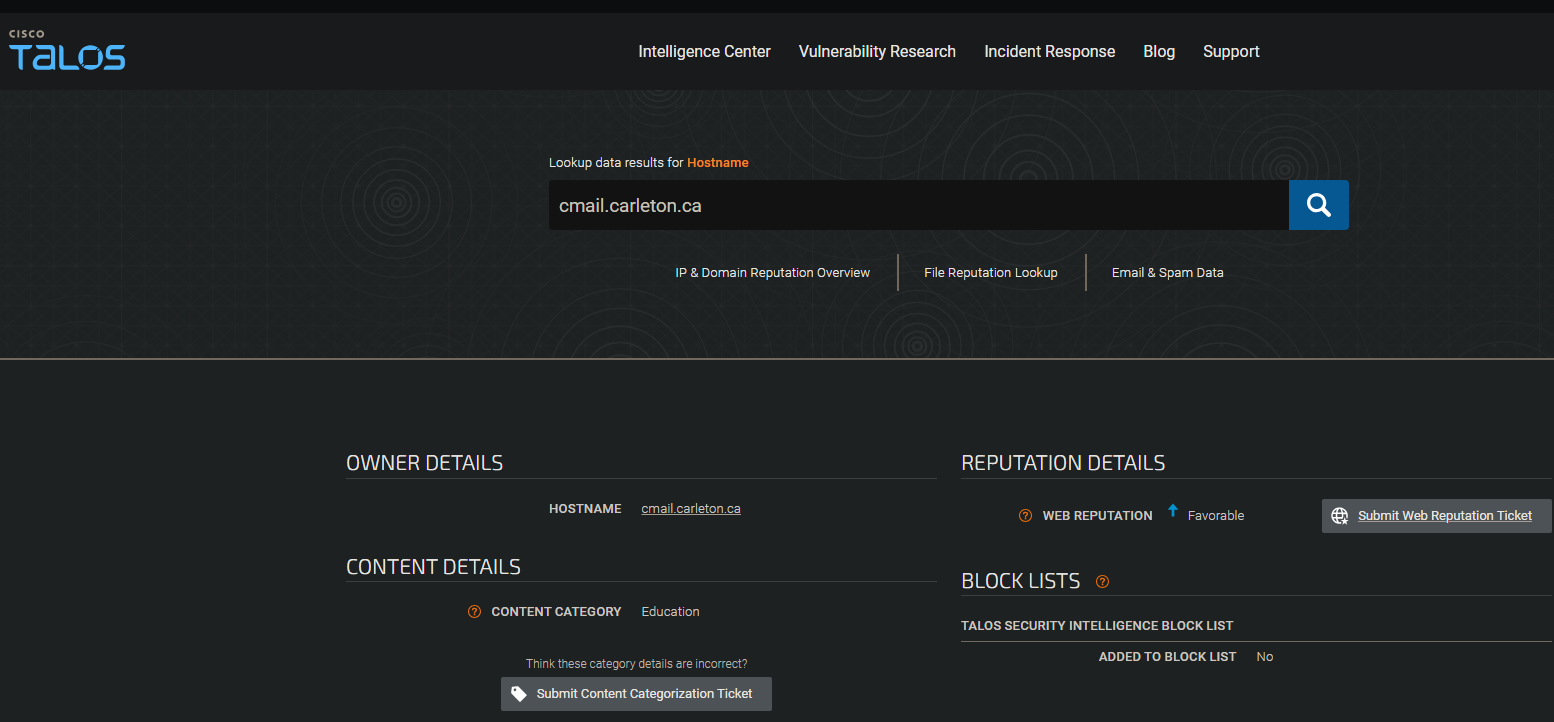 Figure 5 Information related to the sender’s email address domain via Cisco Talos
Further analysis of the domain name reveals it is located in Canada.
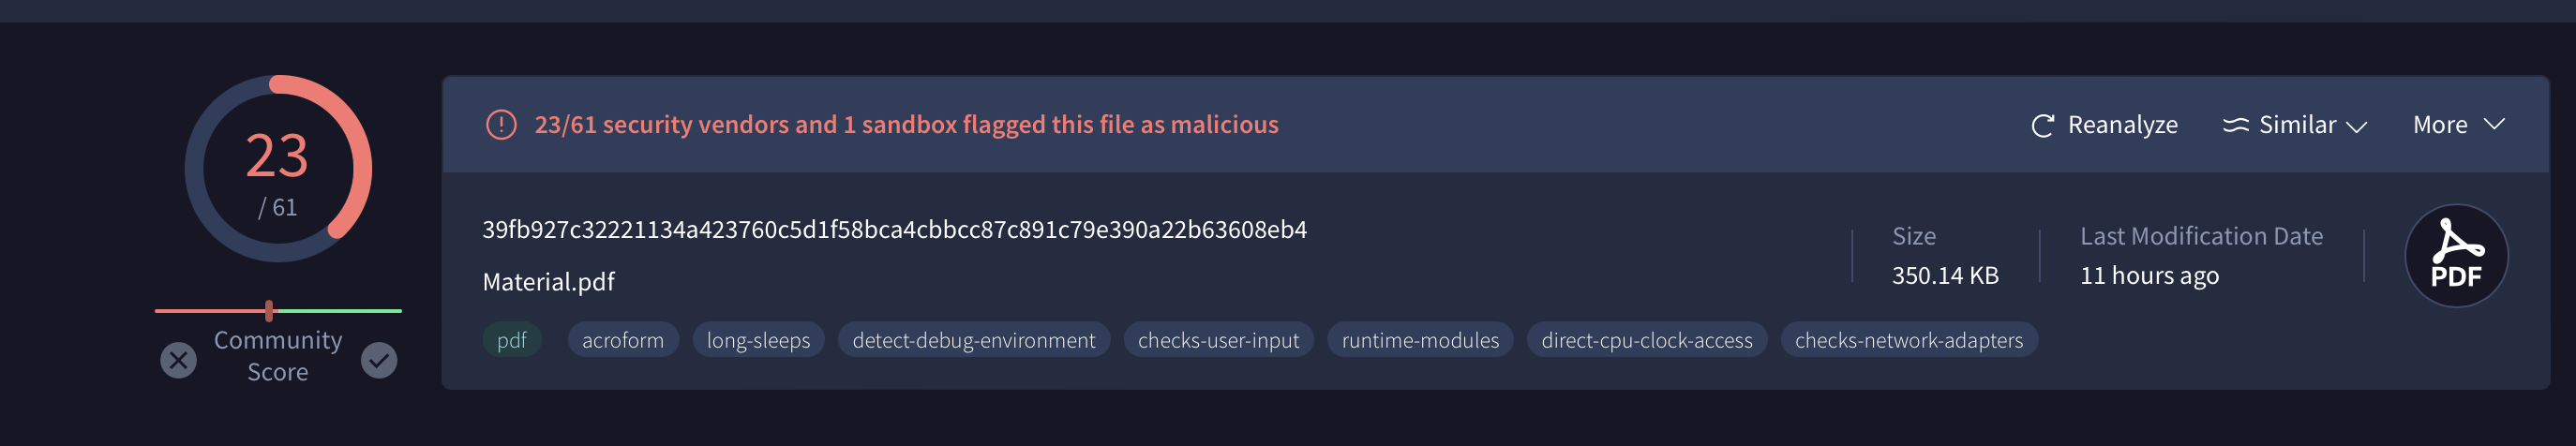 Figure 6 Domain name location via Cisco Talos
The zipped file was downloaded and it contained a Material.pdf file. Moving the file to desktop results in the file requesting the password: infected. The file was unzipped and uploaded in VirusTotal. VirusTotal found the file to be malicious. —
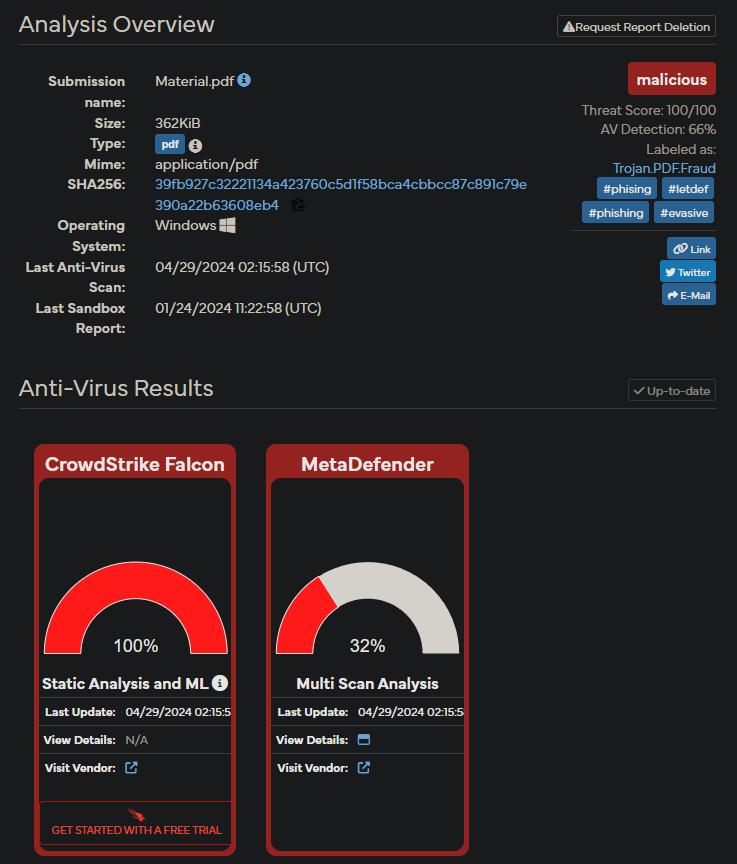 Figure 7 Analysis of the file via VirusTotal
To decrease the chance of a false positive, I uploaded the file to Hybrid Analysis. It also determiend the file was malicious.
 Figure 8 Analysis of the file via Hybrid Analysis
—
##Conclusion
Email was found to contain a malicious attachment. The actions of the sender were blocked and the email was deleted.