SOC141 EventID:86 - Phishing URL Detected [LetsDefend Walkthrough]
Analysis of phishing URL.
Severity Level: High
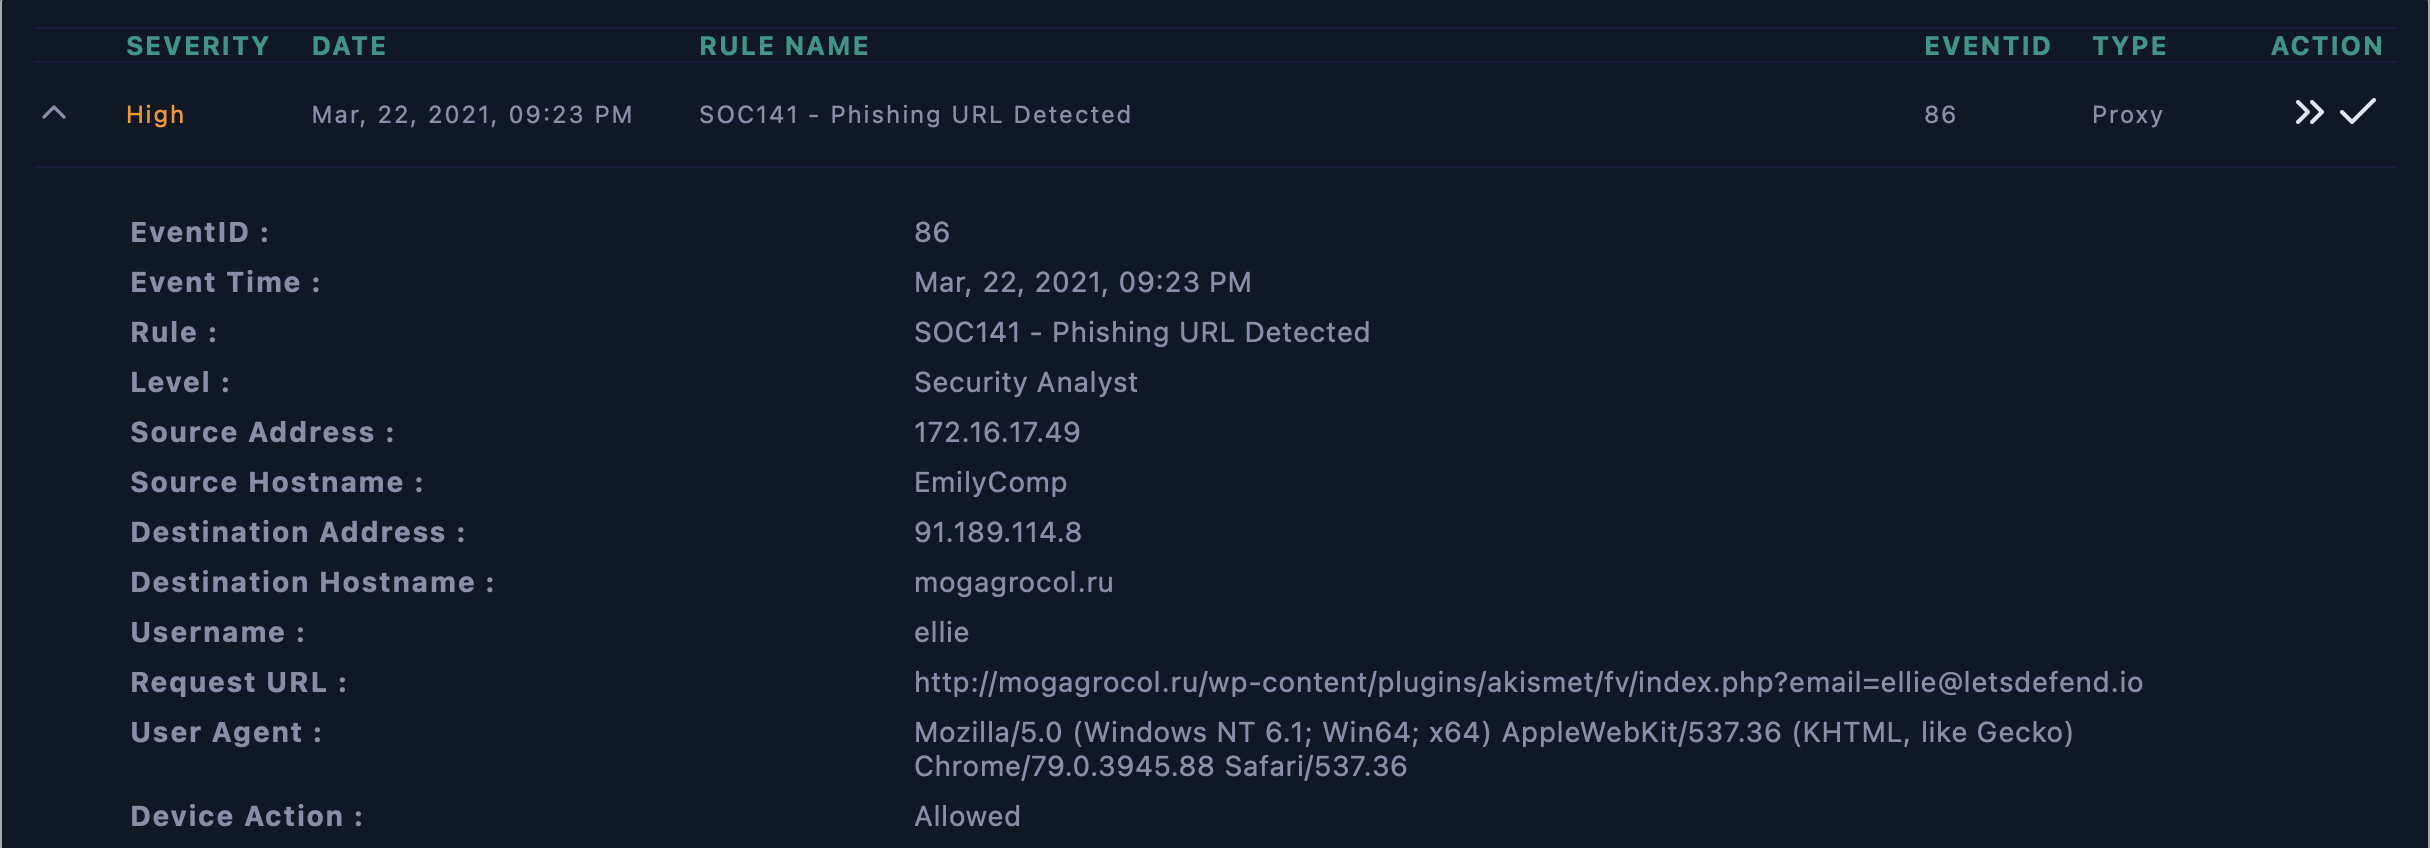 Figure 1 Details of the phishing alert
According to the information provided, on March 22, 2001 at 09:23PM, an event occurred in which a phishing URL was detected. The alert originated from the address 172.16.17.49, from host EmilyComp, username Ellie.
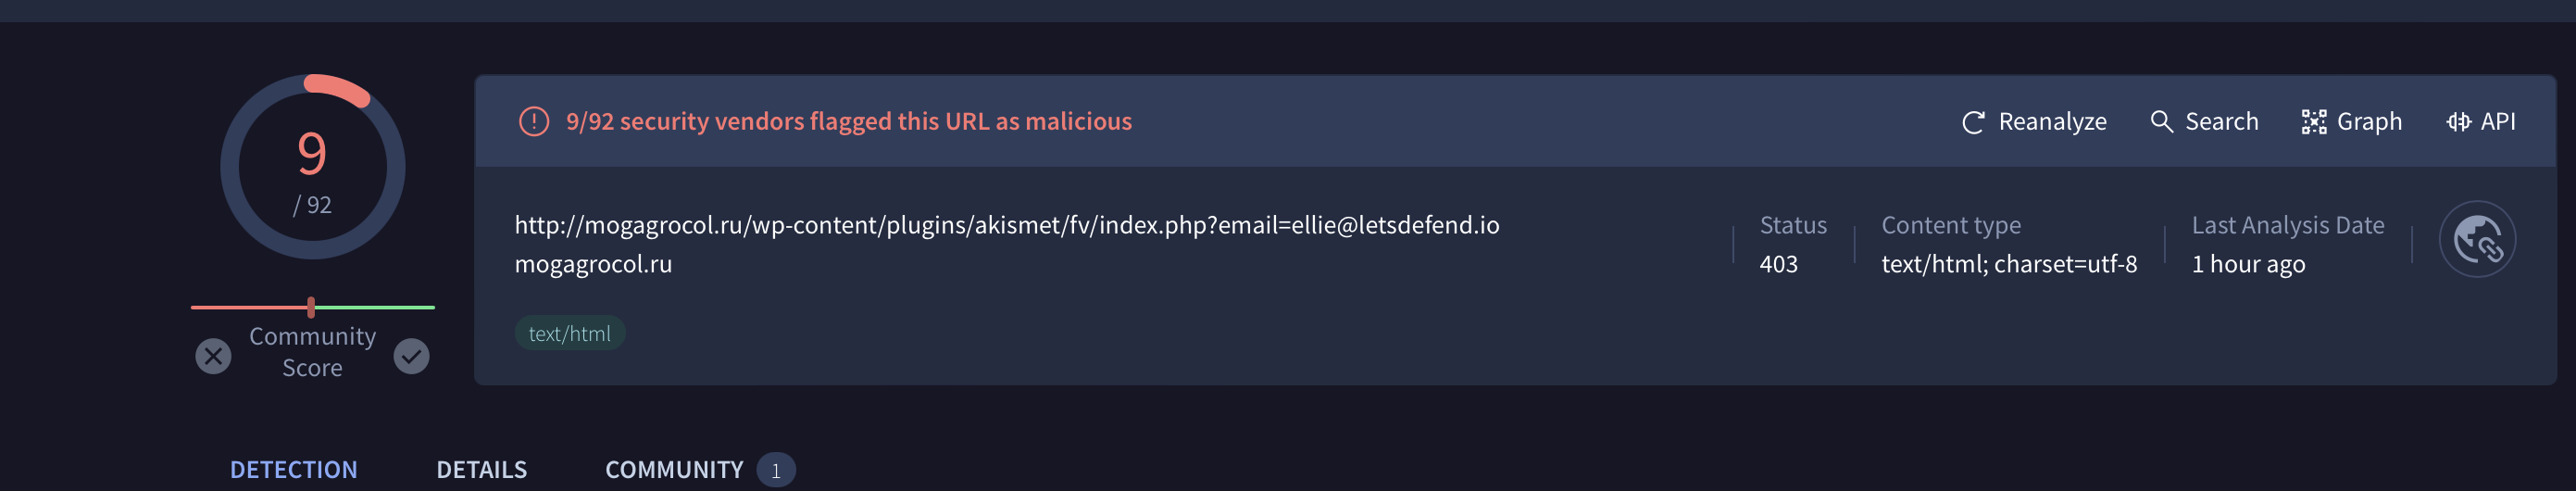 Figure 2 URL analysis results from Virus Total
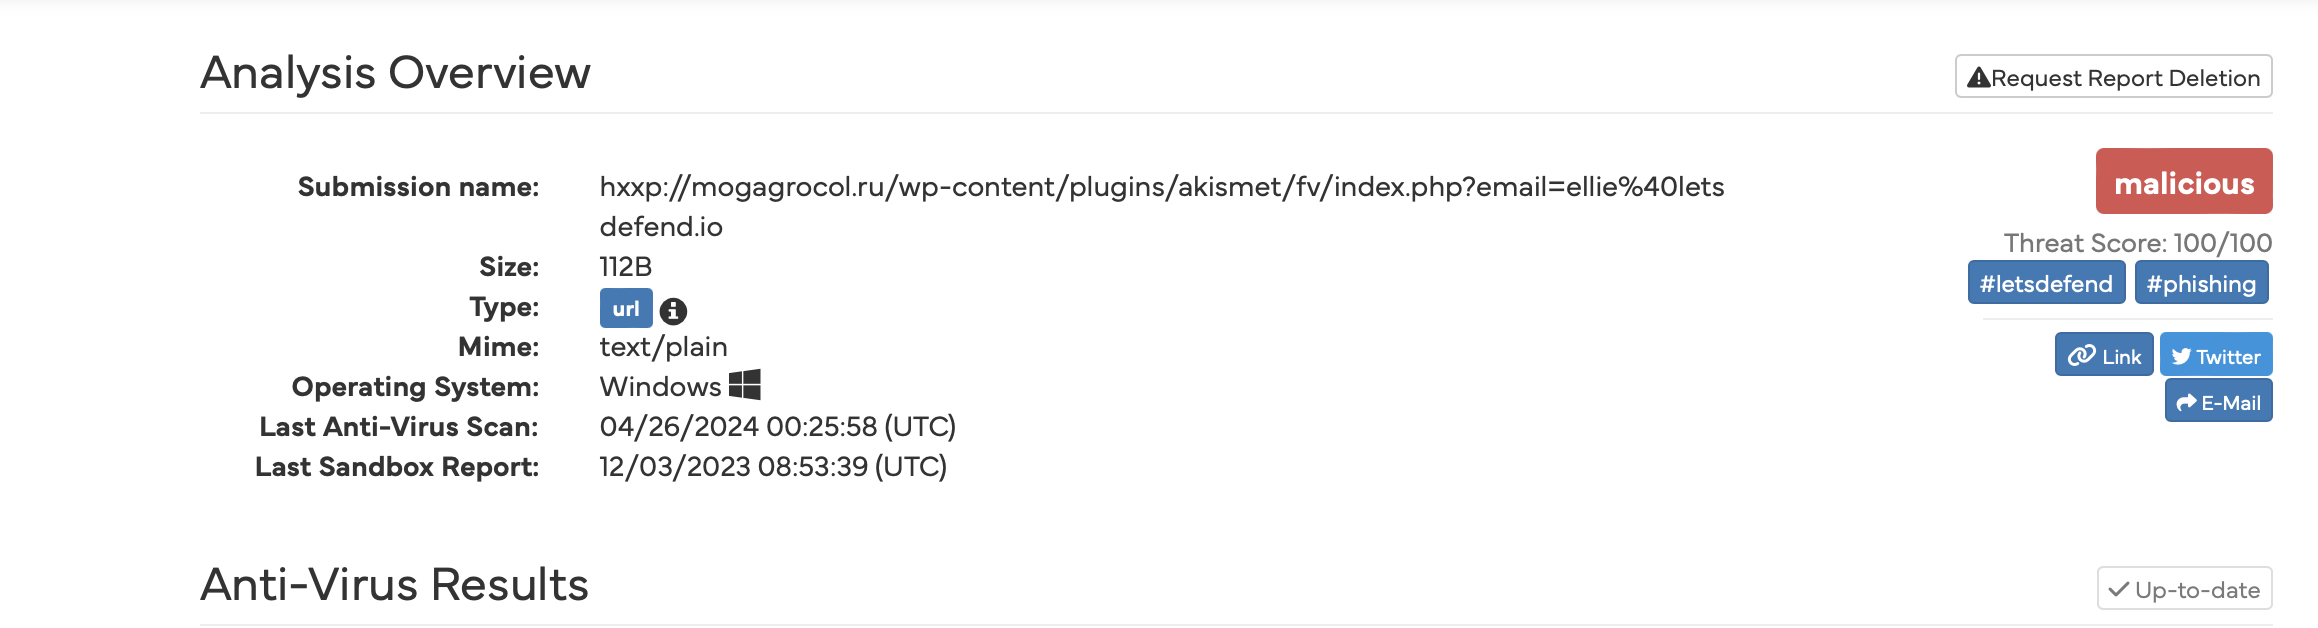 Figure 3 URL analysis results from Hybrid Analysis
As shown in figure 2 and figure 3, the URL was determined to be malicious by VirusTotal and HybridAnalysis. VirusTotal had 9 security vendors flag the URL as malicious.
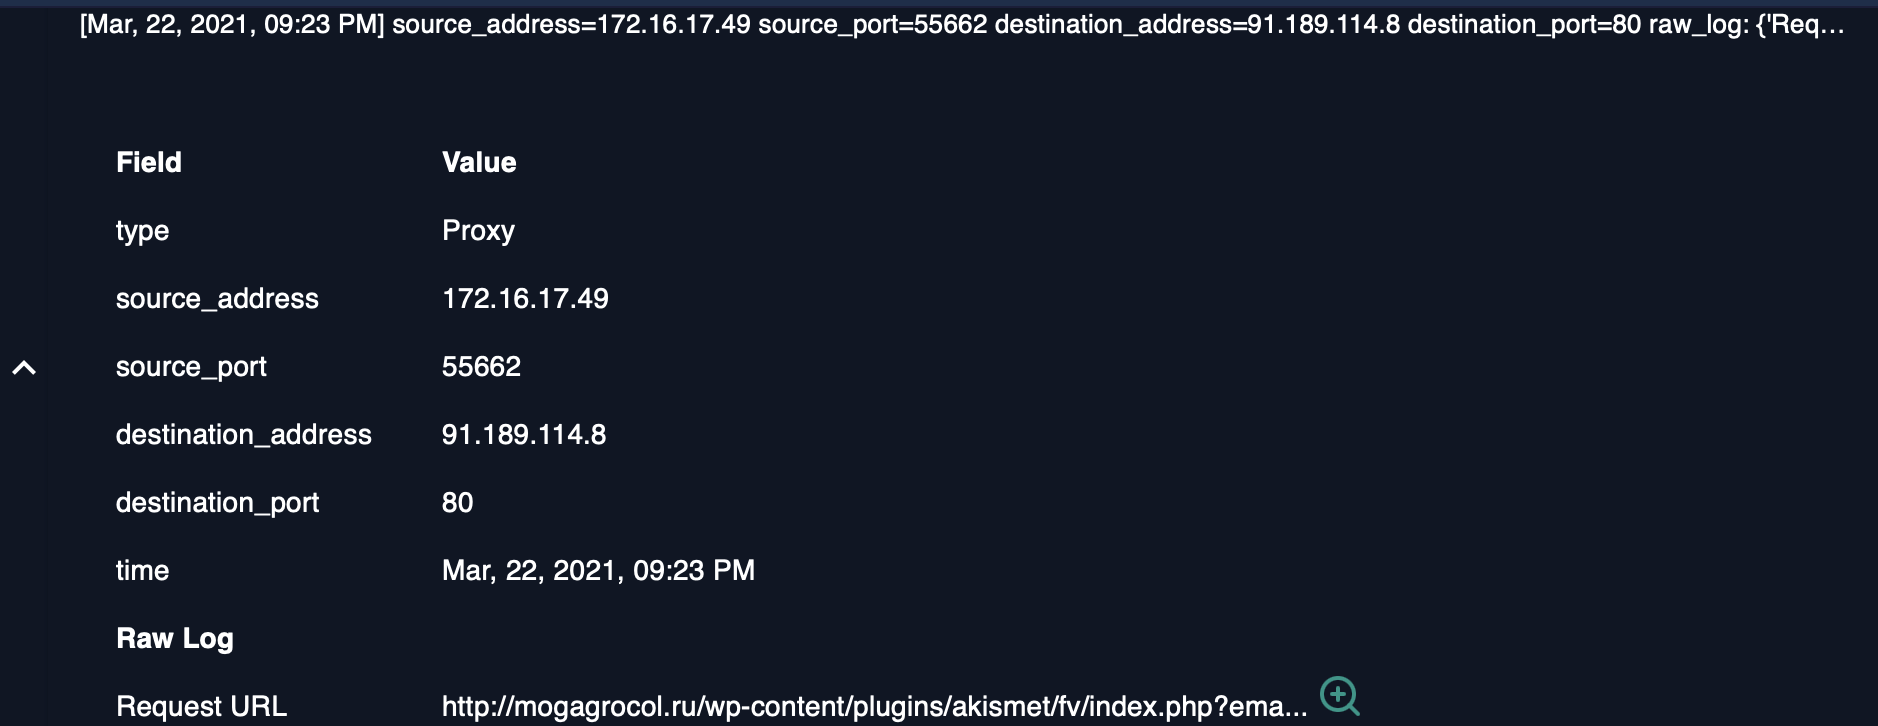 Figure 4 Event log
Inputting the source IP’s address into Letdefend’s Log management section provides several event logs. The event log of interest shown in figure 4, shows the malicious URL is destined to for port 80. Port 80 is an unsecure Hyper Text Transfer Protocol (HTTP), used to transmit and receive unencrypted web traffic. The Request URL uses HTTP, so it was sent to port 80. The action was not blocked,so the host computer will be contained (Figure 5).
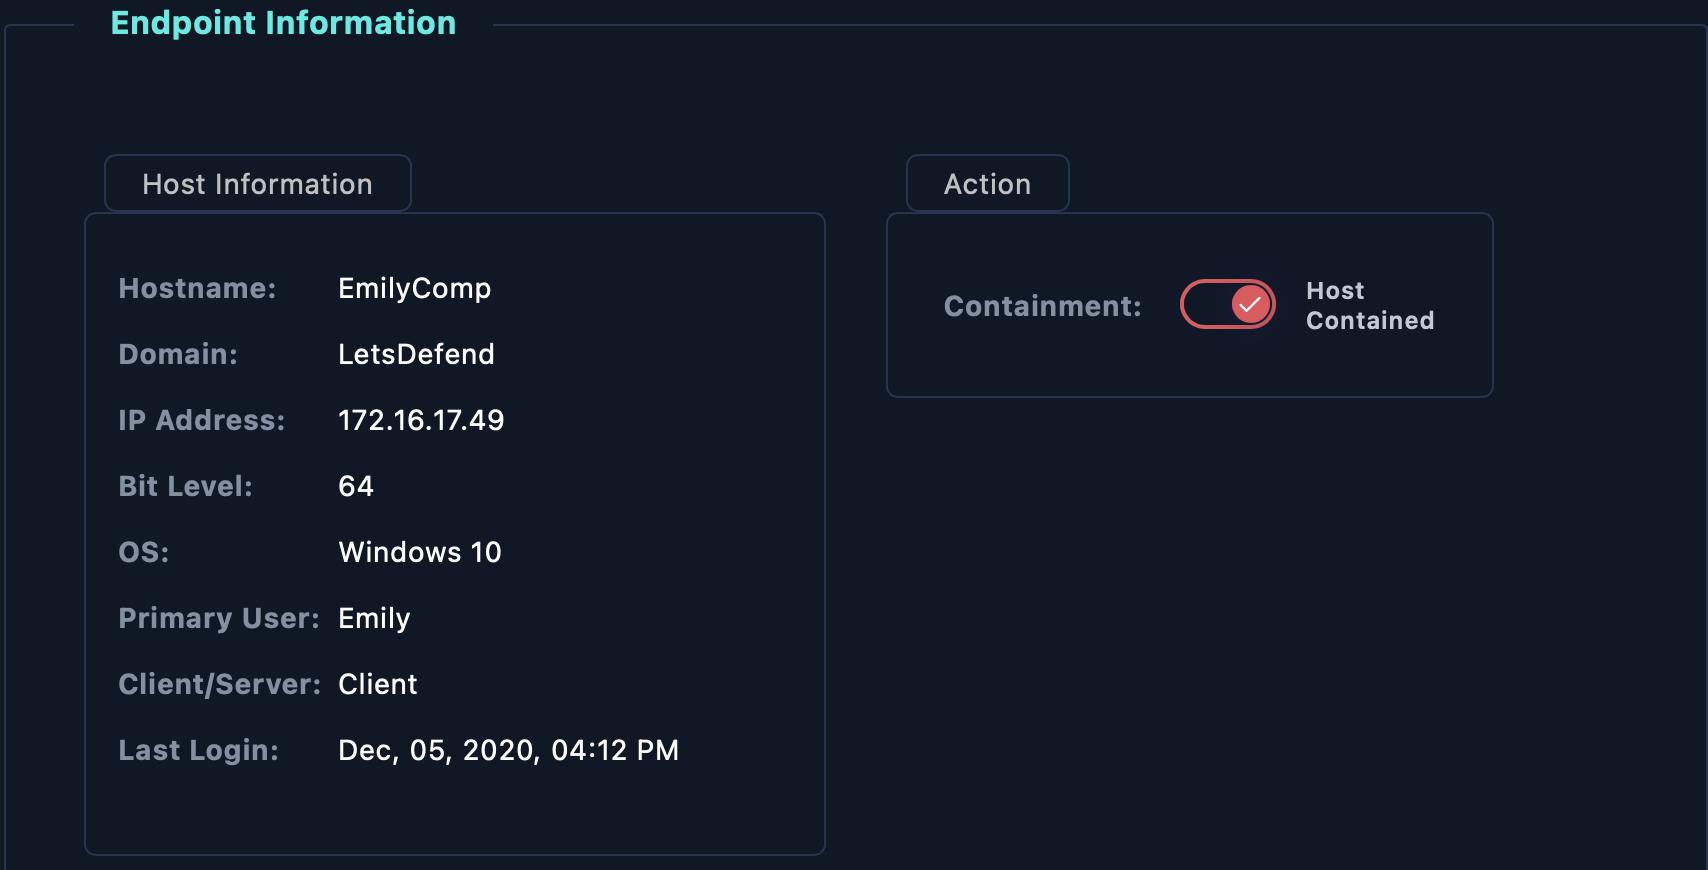 Figure 5 Host Containment